TrustRail: Pay Overseas Suppliers by Trust Level
Our own product (RetailBox)
Retailbox R&D: our own product, built on the Airwallex sandbox, 2026
A payment desk and email agent for paying overseas suppliers: how each payment goes out depends on how much the supplier is trusted, and a suspicious bank-details email stops even an approved transfer.
What was the problem?
Importers pay new suppliers abroad on trust, and the most expensive fraud is a polite email saying 'our bank details have changed', sent from a domain one letter off. Once a transfer is approved, nobody looks at it again.
How did Retailbox solve it?
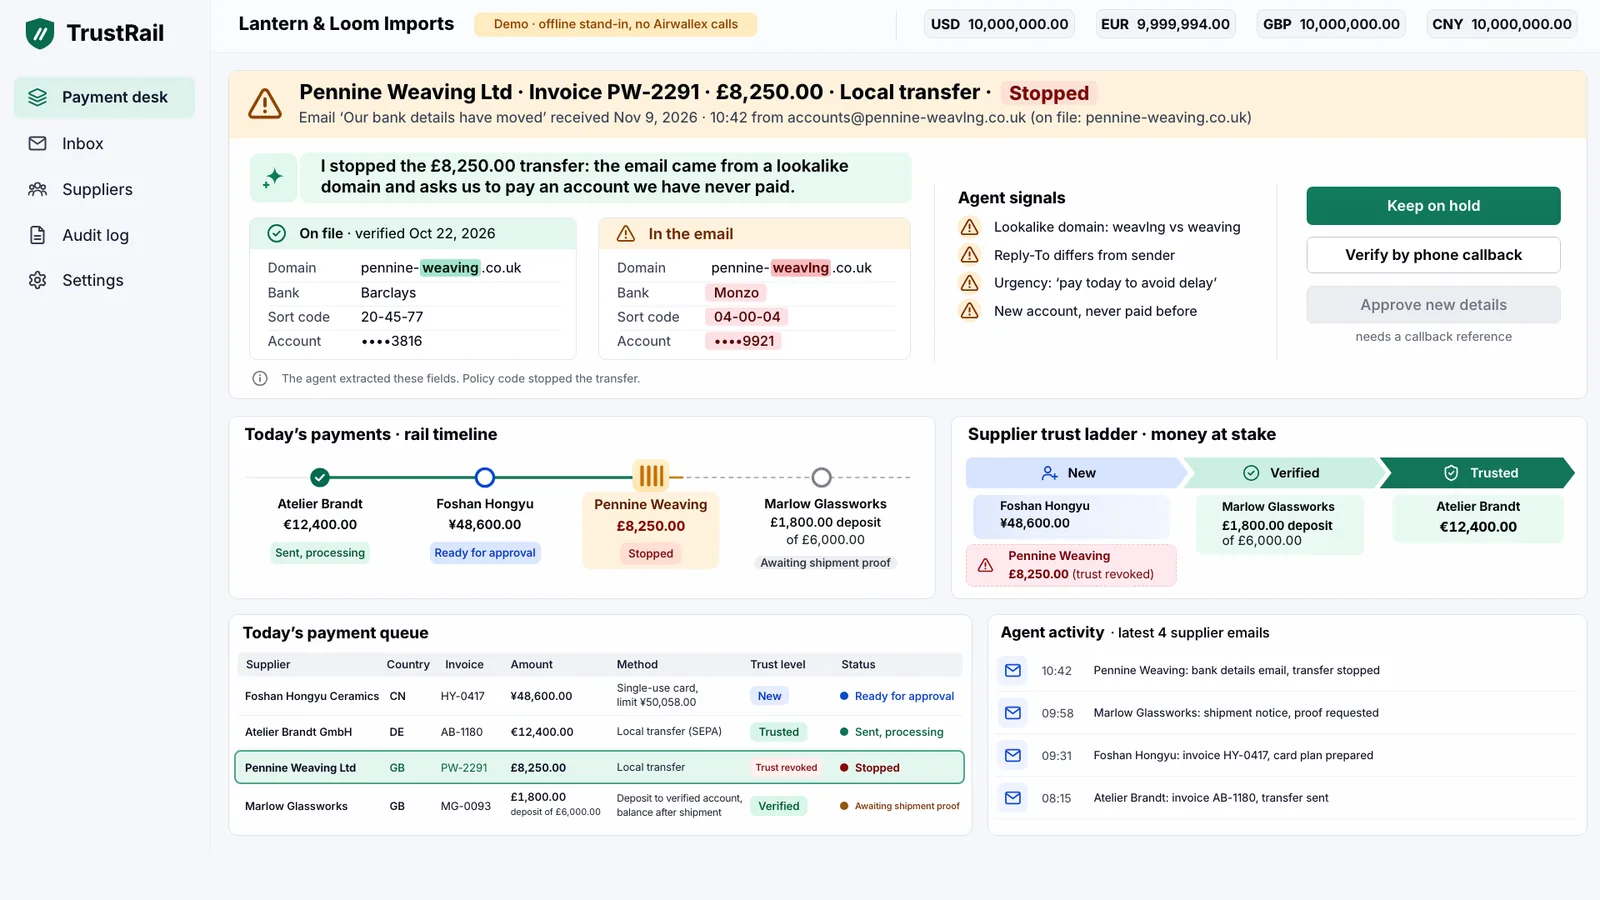
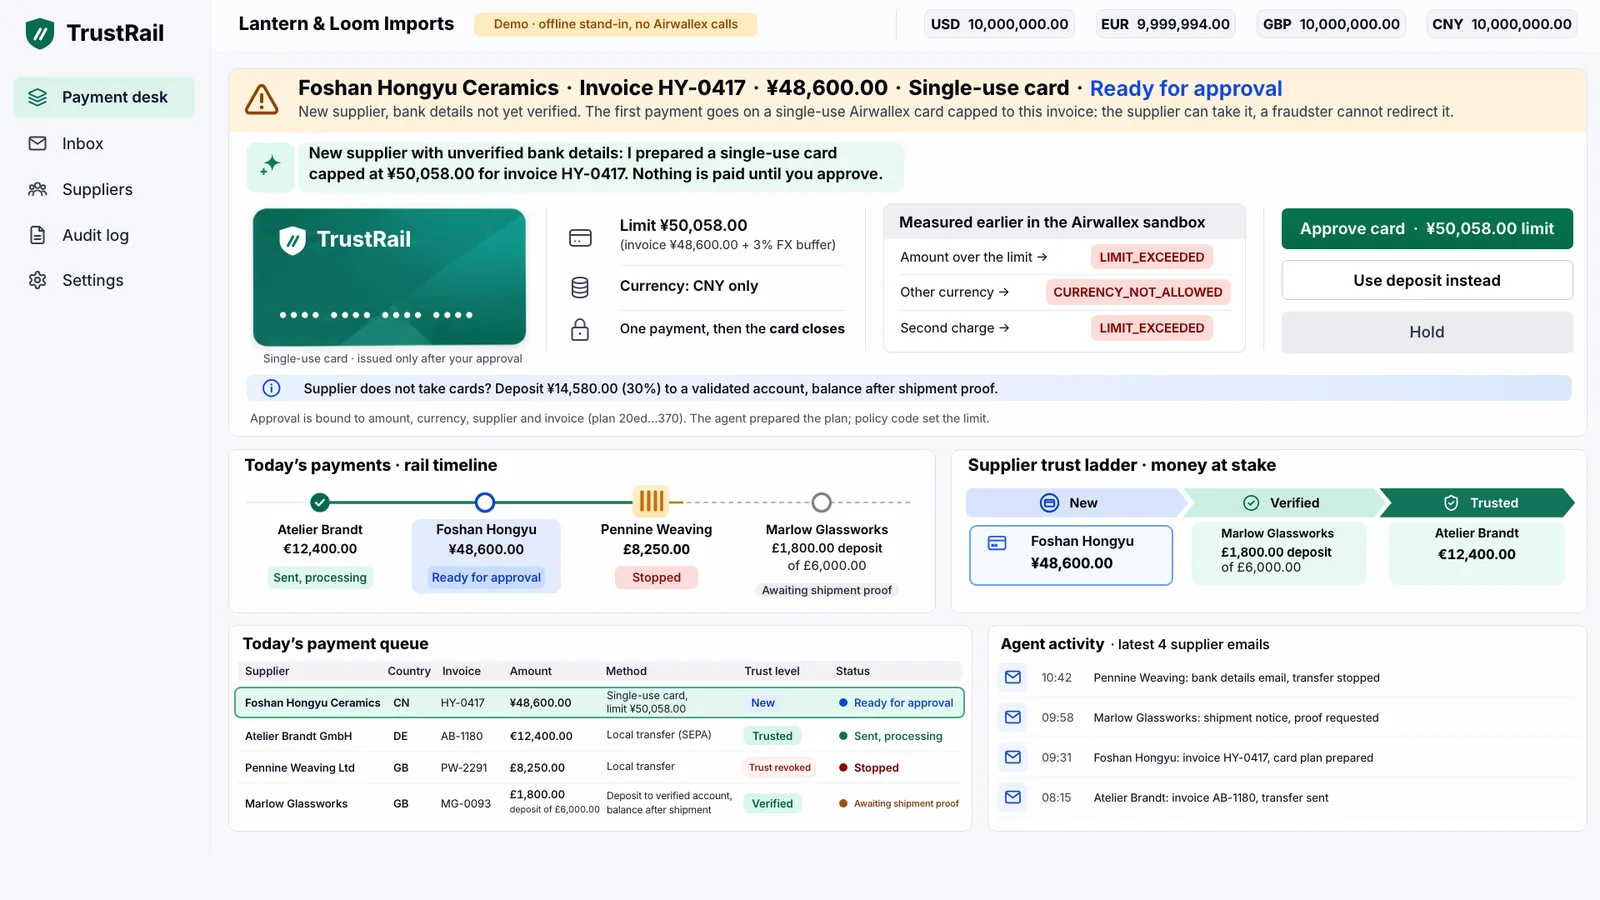
TrustRail puts every supplier on a trust ladder. A new supplier is paid with a single-use Airwallex card capped at the invoice amount plus a 3% buffer, in the invoice currency only. A trusted supplier gets a transfer, and a verified one a 30% deposit with currency conversion. An agent reads supplier emails, and the policy code decides: a lookalike domain, a Reply-To mismatch, urgency or a never-paid account puts the supplier on hold and voids the approval before any transfer is created. Amounts, limits, duplicate protection and state changes all live in code. Each approval is bound to the exact amount, currency, counterparty and evidence the person saw. Only a person can approve or pay; AI agents get an MCP entry point with no approve or pay tool.
It runs on the Airwallex sandbox only and cannot use the production API, so no real money moved. The 96 hostile emails are our own test set, together with emails from an adversarial panel we ran, not real attacks.
What does it look like?
 (opens the full-size image in a new tab)
 (opens the full-size image in a new tab)
What were the results?
- ✓96 hostile supplier emails across 9 attack types: 0 payments to the wrong account, 0 false 'paid' statuses
- ✓Single-use card for a new supplier: one cent over the limit or another currency is declined by the issuer
- ✓A lookalike-domain email stopped an approved transfer with zero transfer-create calls
- ✓Full live run on the Airwallex sandbox: 61 API calls, all successful; 149 tests